
The coding harness that won't turn on you.
Symbiotic Code keeps AI coding in check. It enforces your security policies, fixes vulnerabilities as code is written, and blocks malicious intent. Your developers won't notice. Your security team will.
npm i -g @symbioticsec/codeInstall the IDE extension or download the CLI to get started for free
Works everywhere you work:
Generate secure code and fix vulnerabilities right where you work. Pay down your security debt and learn secure coding with just-in-time exercises.
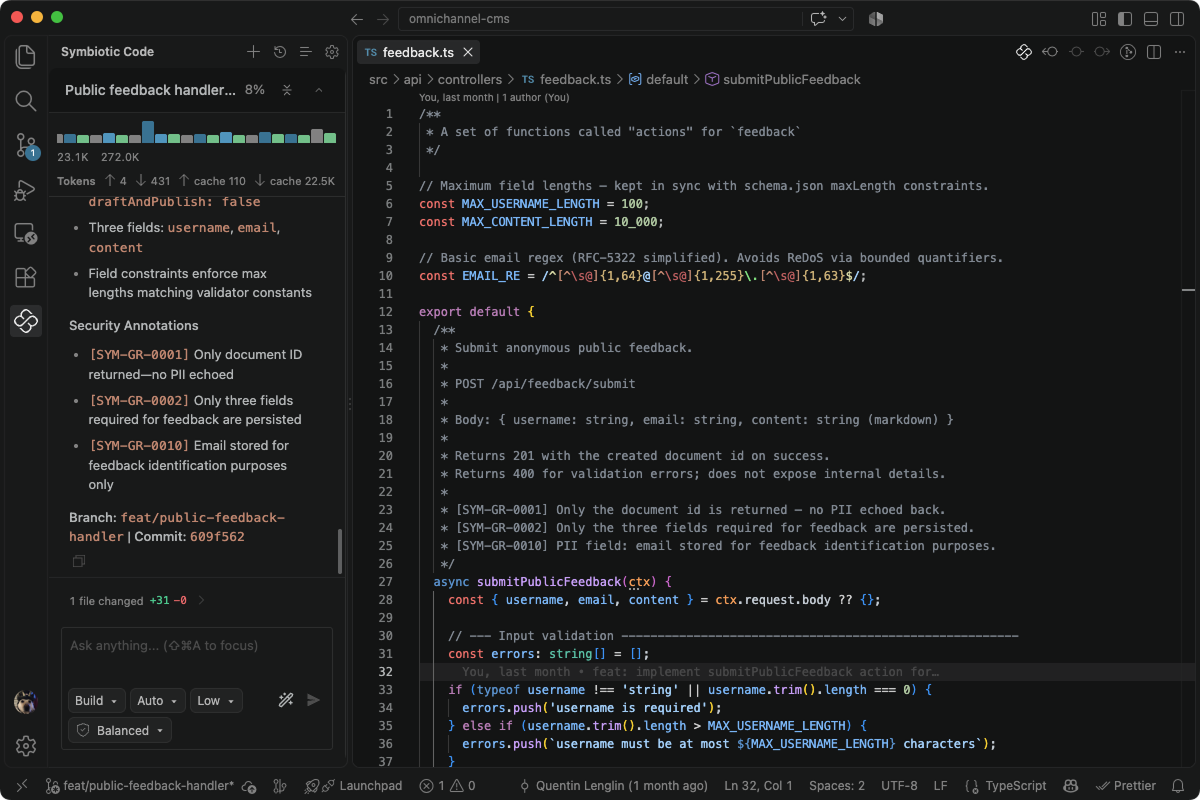
Developers keep the speed. Security keeps the control.
Your workflow, minus the rework.
Traditional AI coding agents lack built-in security, forcing developers to blindly trust tools that generate 5.5x more critical vulnerabilities.
Symbiotic Code runs security at generation time, eliminating manual overhead, rework tickets, and redundant PR passes.
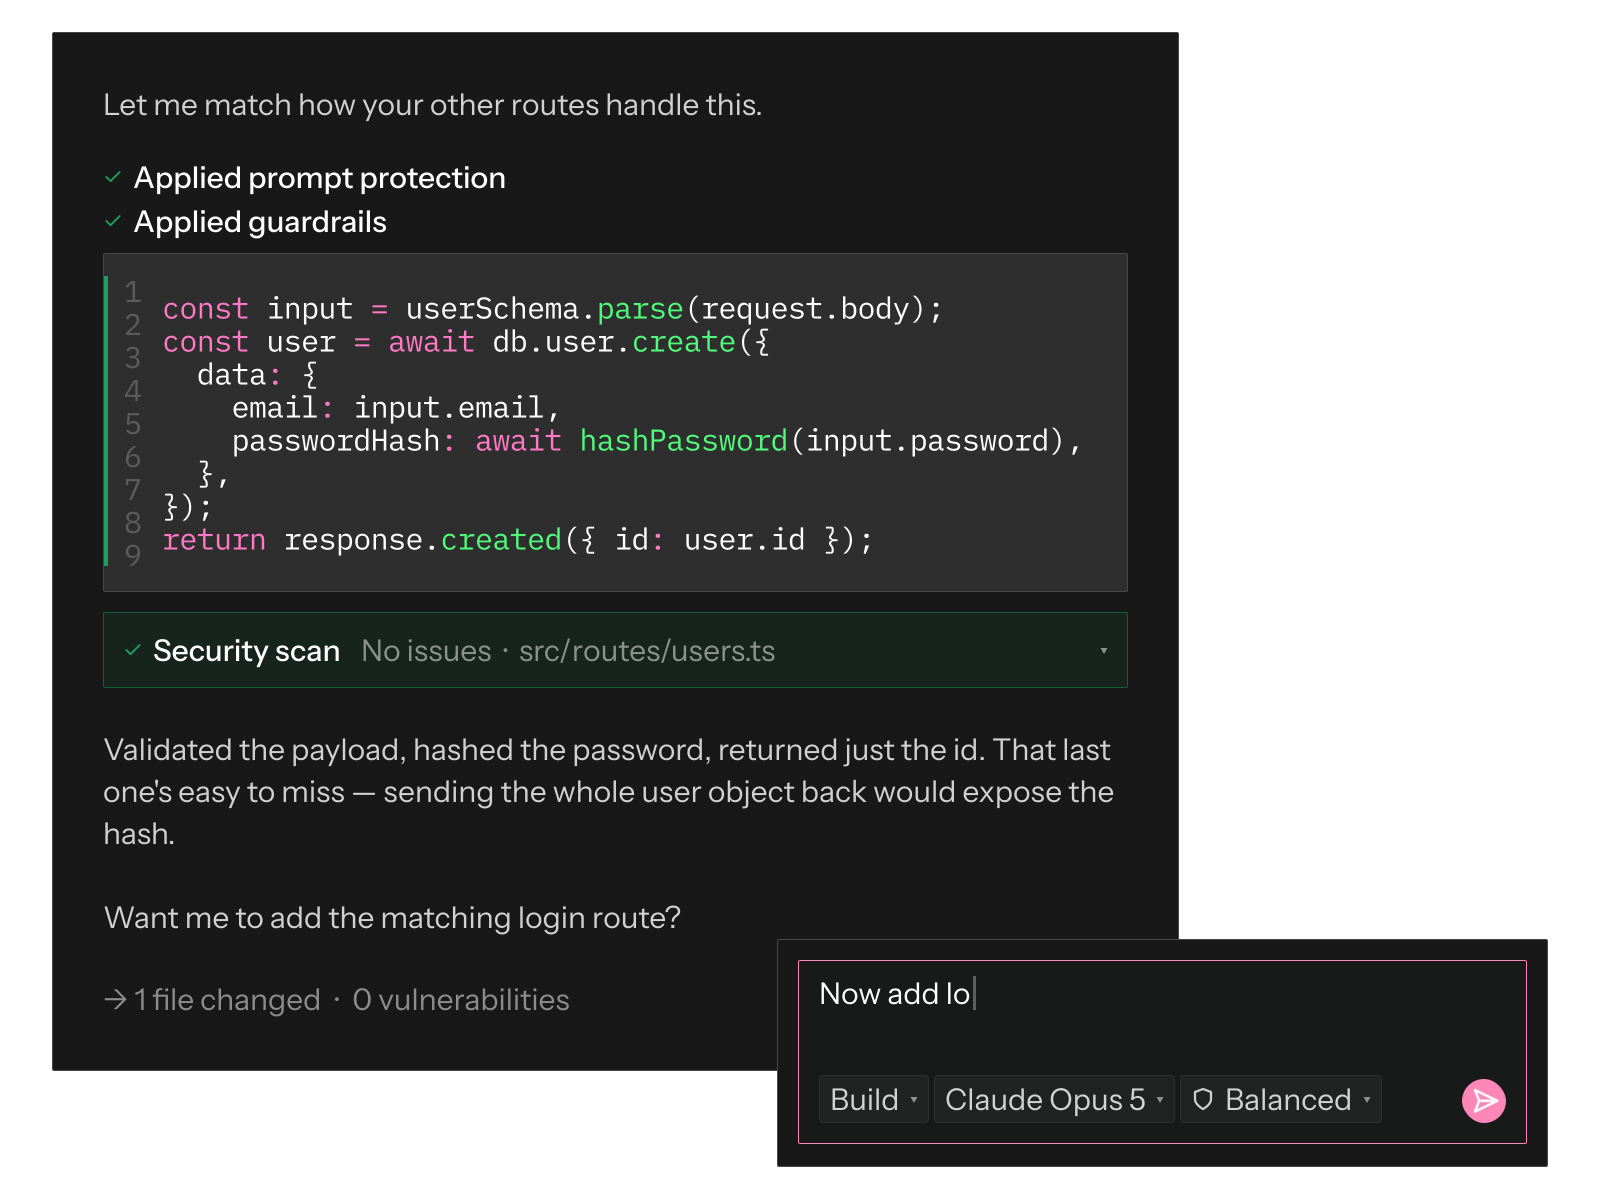
And everything you need from a coding agent, right out of the box:
Ask, plan, build, debug
Explore the codebase read-only, agree on the approach, then let the agent change files.
Speaks your language server
The right LSPs load automatically, so the model sees what your editor sees and makes fewer mistakes.
Any model, your keys
Claude, GPT, Gemini, or SLMs, on our cloud, yours, or on-prem, with auto-select picking the model for the task.
Agents in parallel
Run several sessions on the same project at once, each with its own task and context.
Hundreds of community plugins
Fully compatible with the OpenCode ecosystem: memory, hooks, flows, etc., all running under the same policies as the agent.
Your policy, enforced before the code exists.
Every coding agent your developers adopt is a new source of vulnerabilities your scanners find after the fact, and a new runtime nobody governs.
Symbiotic Code enforces your policy at generation time and runs the agent under your rules, so the backlog stops refilling and AI coding becomes safe.
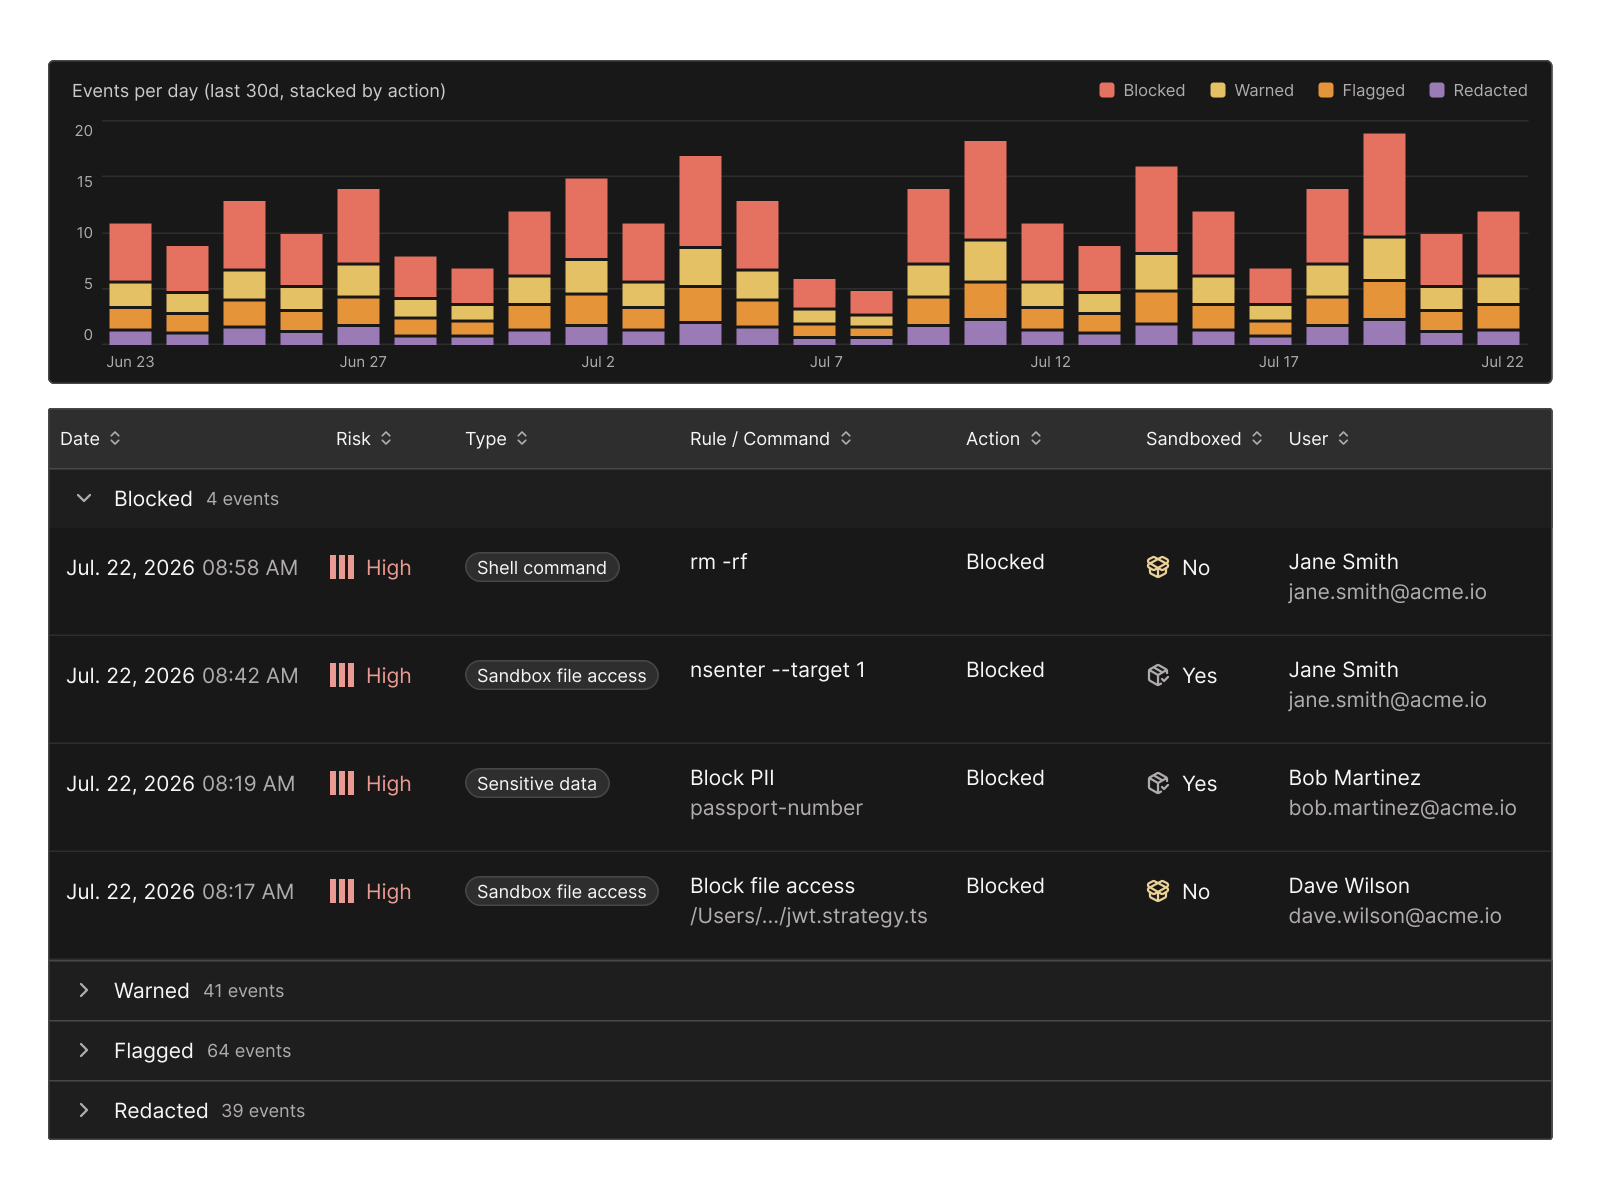
All the tools you need to secure your AI coding practice:
Code born secure
Vulnerabilities, vulnerable dependencies, hard-coded secrets, and authentication and authorization gaps get fixed while the agent writes.
Control the ecosystem
Allow-list or deny-list plugins, skills, and MCP servers. Or leave the call to the agent, and it scans each external tool before using it.
Harden the agent
Sandboxed runtime, a network policy you define, and destructive commands blocked by default.
Guardrails applied, and verified
Drop in your existing documentation, let the agent discover rules from the codebase, start from an industry template, or click through our technical guidance.
Secure the prompt
Protect against leaks of PII, credentials, and confidential information, and defeat adversarial prompting with intent detection.
Access the models you love, keep your costs down with turn-by-turn smart routing, and bring your own LLM for privacy


By securing AI output at the source, Symbiotic Code removes that friction, allowing teams to move at full speed without compromising safety. It’s a game-changer for any organization looking to scale AI-driven development with total confidence.
Julien Launay, CEO & Co-founder @ AdaptiveML
Security in every place your team writes code
The agent isn't the only place code gets written. Symbiotic catches vulnerabilities in your editor and on the pull request too.
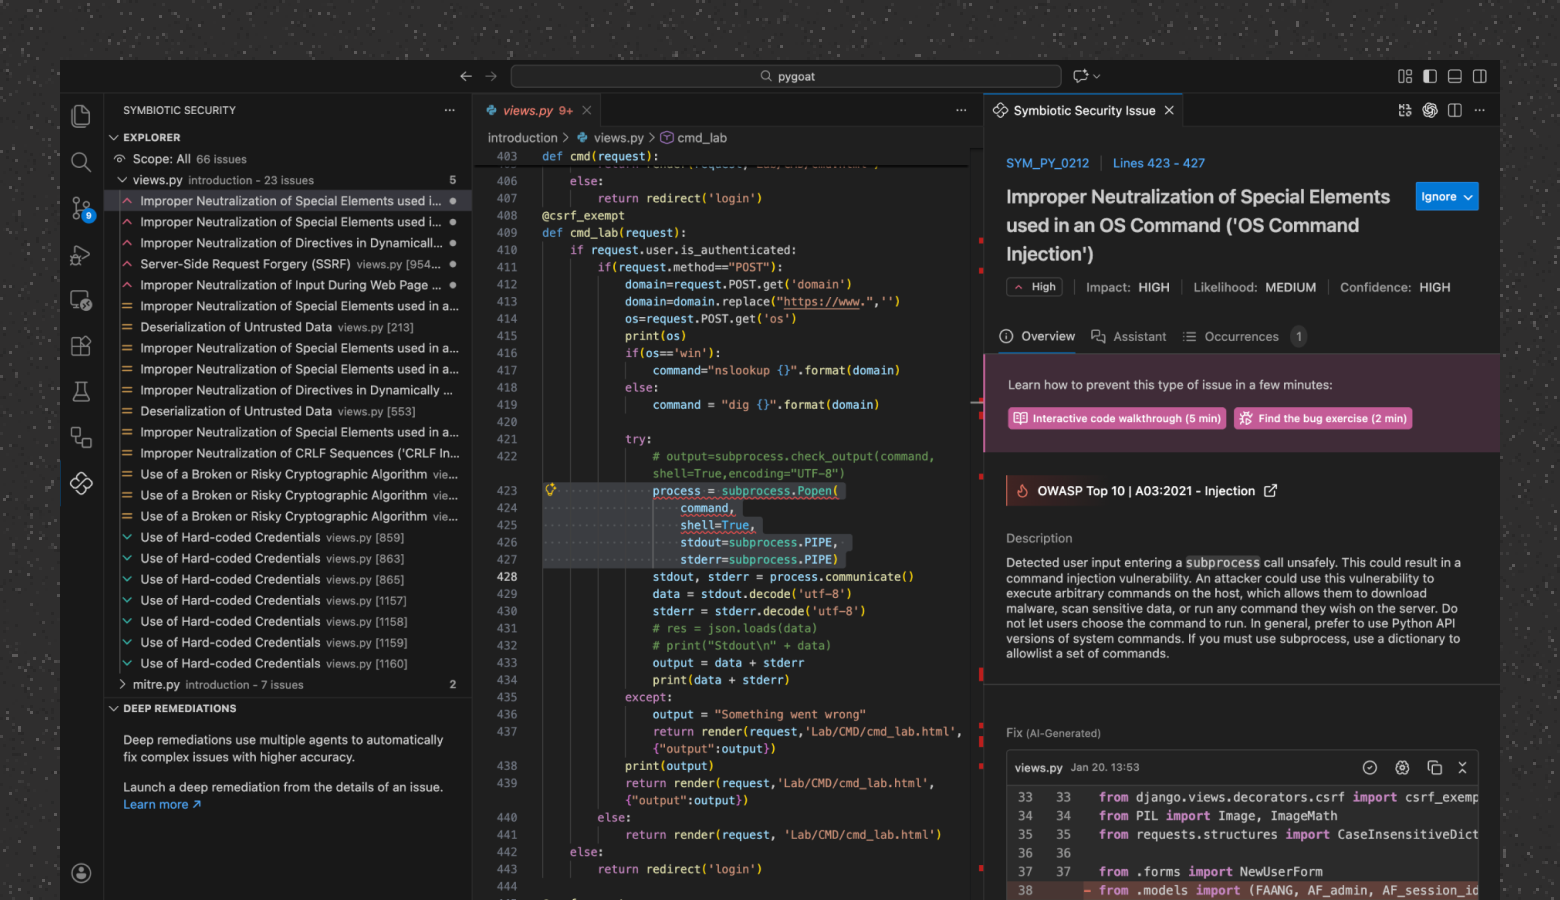
Catch vulnerabilities as you type
The Symbiotic extension doesn’t only generate secure code: it also flags vulnerabilities the moment you write them yourself. It marks the issue, provides training, and offers the fix in one click. Complex ones go to deep remediation, with complex reasoning and multi-agent capabilities.
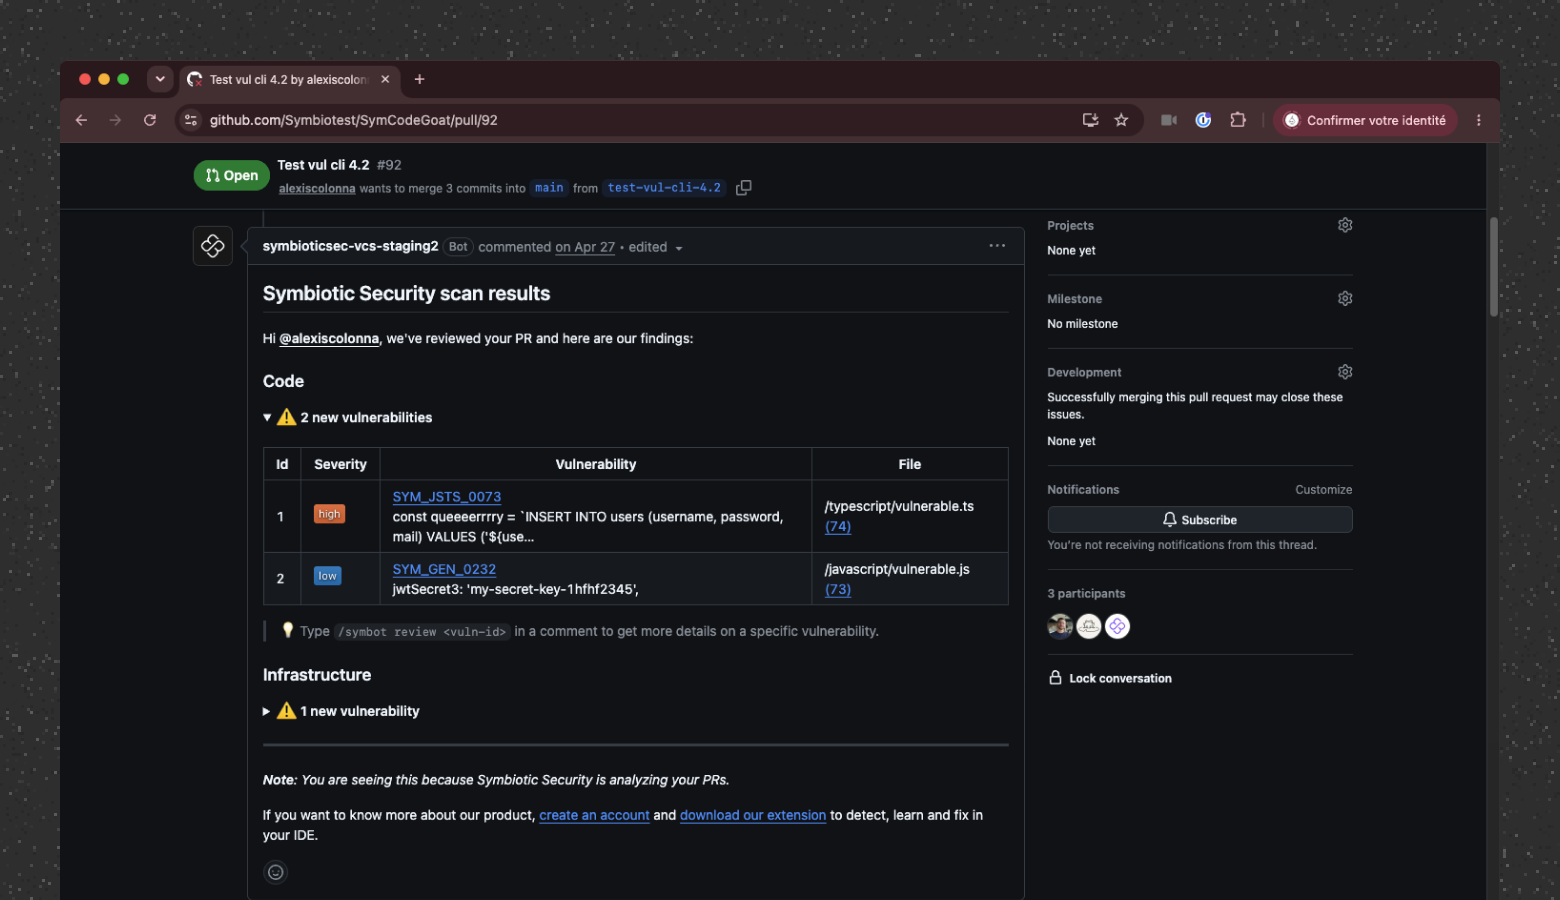
Stop vulnerabilities before they merge
Connect your GitHub or GitLab org and Symbiotic reviews every pull request, code and infrastructure alike. Findings land in line with a remediation attached. You set the policy for which severities hold a merge and which go through, and the review enforces it.
Already using another coding agent?
Switching to Symbiotic takes minutes. Bring your skills, MCP servers, and model preferences over. Nothing's lost, and the workflow is the one you already know.
Questions & answers
Will this slow my developers down?
The opposite. In practice, security runs at generation time, so code arrives clean on the first pass: fewer review loops, no scan-fix-regenerate cycle, no rework tickets.
What's the difference between a coding harness and a coding agent?
An agent writes code. A harness runs the agent inside a loop you define: policies applied before generation, verification after, and a sandbox around every action. Symbiotic Code is the harness; the models are whichever you pick.
Does it work on code my team writes by hand?
Yes. The IDE plugin, PR apps, and CI integration scan and fix any code in the repo, not just what the agent produced.
What happens to my CLAUDE.md, skills, and MCP servers?
They carry over as-is. Most developers are productive within a few minutes.
GENERAL
Will this slow my developers down?
The opposite. In practice, security runs at generation time, so code arrives clean on the first pass: fewer review loops, no scan-fix-regenerate cycle, no rework tickets.
What's the difference between a coding harness and a coding agent?
An agent writes code. A harness runs the agent inside a loop you define: policies applied before generation, verification after, and a sandbox around every action. Symbiotic Code is the harness; the models are whichever you pick.
Does it work on code my team writes by hand?
Yes. The IDE plugin, PR apps, and CI integration scan and fix any code in the repo, not just what the agent produced.
What happens to my CLAUDE.md, skills, and MCP servers?
They carry over as-is. Most developers are productive within a few minutes.